Managed IT for 1–50 people

The IT department you don’t have to hire.

Laptops, logins, backups, the firewall and the printer that stopped — handled by one person who knows your setup, for less than a junior hire costs you in a quarter.

No long contracts. Month to month after the first 90 days.

Included every month

  • Every device, patched and trackedOnboarding, offboarding, and knowing which laptop went home with whom.
  • Security that survives an auditMFA everywhere, tested backups, and a written answer for your insurer.
  • AI your team will actually useTools chosen for your workflows, with guardrails on what data leaves the building.
  • A person, not a ticket queueThe same number, the same voice, every time something breaks.
Works with
  • Google Workspace
  • Microsoft 365
  • macOS
  • Windows
  • AWS

What’s covered

Everything a 30-person company needs from IT.

Not a menu of add-ons. One monthly scope that covers the things that actually break, plus the things that quietly don’t until they do.

Devices and people

  • Laptop setup, encryption and patching — Mac and Windows
  • New-hire onboarding: accounts, apps, hardware, day-one working
  • Offboarding that actually revokes access the same day
  • An asset list you can hand to your accountant or your insurer

Identity and email

  • Google Workspace or Microsoft 365 administration
  • MFA enforced, shared logins retired, admin access limited
  • Mail authentication — SPF, DKIM and DMARC set up properly
  • Groups, aliases and permissions that match how you actually work

Network and infrastructure

  • Firewall, Wi-Fi and VPN configuration and monitoring
  • Cloud infrastructure on AWS — built, documented, and yours
  • Backups that are tested, not just scheduled
  • Documentation so nothing lives only in one person’s head

Day-to-day support

  • One number and one inbox — you reach me, not a queue
  • Remote support for the whole team
  • Vendor wrangling: ISPs, software renewals, hardware orders
  • A standing monthly check-in on what’s coming next

Security

The questions your insurer is about to ask.

Cyber insurance applications and client security questionnaires ask the same dozen things. Most small companies discover they can’t answer them at renewal time, under deadline. The point of doing this properly is that the answers already exist.

  • Multi-factor authentication enforced across email, cloud and remote access
  • Backups running, encrypted, and restore-tested — not just green in a dashboard
  • Endpoint protection deployed and monitored on every machine
  • Patch levels tracked, with a record of what was updated and when
  • Access reviews: who can reach what, and why they still need to
  • Phishing training that isn’t just an annual video nobody watches
  • A written incident plan, so nobody is improvising at 2am

AI

Useful, and not a data leak.

Your team is already pasting company information into chatbots. The choice isn’t whether AI enters your business — it’s whether it does so on terms you set.

  • A tool selection that fits your actual workflows, not the hype cycle
  • Business-tier accounts, so your data isn’t training someone’s model
  • Clear rules on what can and can’t be pasted into a prompt
  • Practical automation for the repetitive work: quotes, intake, summaries, scheduling
  • Training that assumes your team is busy, not that they’re engineers

How it works

Three steps, no surprises.

  1. 01

    A 20-minute call

    You tell me what you’re running and what’s been breaking. I tell you whether I’m the right fit. If I’m not, I’ll say so on the call.

  2. 02

    A two-week audit

    I map what you have — devices, accounts, backups, network, exposure — and hand you a written findings document. It’s yours whether or not we go further.

  3. 03

    Monthly coverage

    A flat monthly fee based on seats, quoted after the audit so it reflects your real environment. First 90 days sets the baseline; month to month after that.

Pricing is per seat, quoted after the audit so it reflects what you actually run.

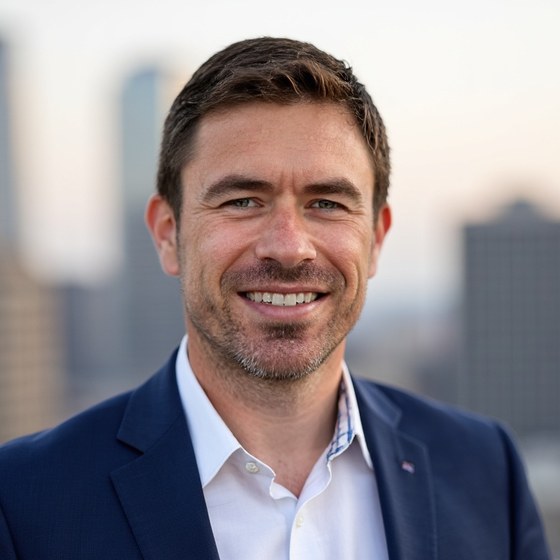
Patrick Danielewski, founder of Fractional Tech Office

Who you’re actually hiring

Patrick Danielewski

Founder & Fractional CTO/CIO

Fractional Tech Office is deliberately small. When you call, you get me — not a rotating tier-one queue reading from a script that doesn’t know your network.

That’s the trade. A large MSP has more hands; I have your whole environment in my head. For a company of 1 to 50 people, the second one is usually worth more.

Twenty-five years of this, at companies from thirty people to several thousand. The large ones taught me what good infrastructure looks like when it’s properly funded. The small ones taught me what it actually costs when there isn’t any.

I work cloud-first and people-first. Technology should be secure, and it should stay out of the way of the people trying to use it — those two goals are not in tension nearly as often as vendors would like you to believe.

Twenty minutes, no deck.

Tell me what you’re running and what keeps breaking. If Fractional Tech Office isn’t the right fit, I’ll tell you that on the call.

Book a 20-minute call

Or reach me directly: patrick@fractionaltechoffice.com · 512-222-1263